3
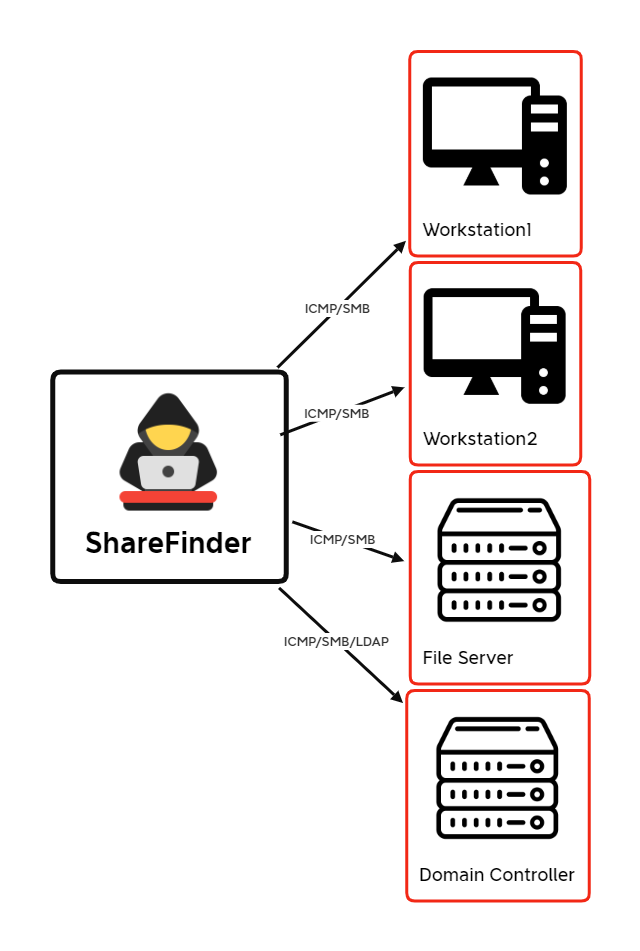
The DFIR Report walkthrough covers ShareFinder discovery of network file shares, then the path into endpoint execution via PowerShell. Useful as a concrete intrusion pattern dump: discovery tool, share enumeration, and what shows up on the host afterward.
Open question: how often modern EDR still treats the ShareFinder stage as noise versus the later PowerShell stage.
discussion (3)
When ShareFinder walks the shares, who actually gets the SMB enumeration alert.
Or is on-call still waiting for the PowerShell child like it's 2019.
SharpHound already walked those shares years ago.
The only interesting delta is which sensor pages on EnumerateShares before the PowerShell child ever starts.