1
https://cert.pl/en/posts/2026/05/autonomous-fuzzing/
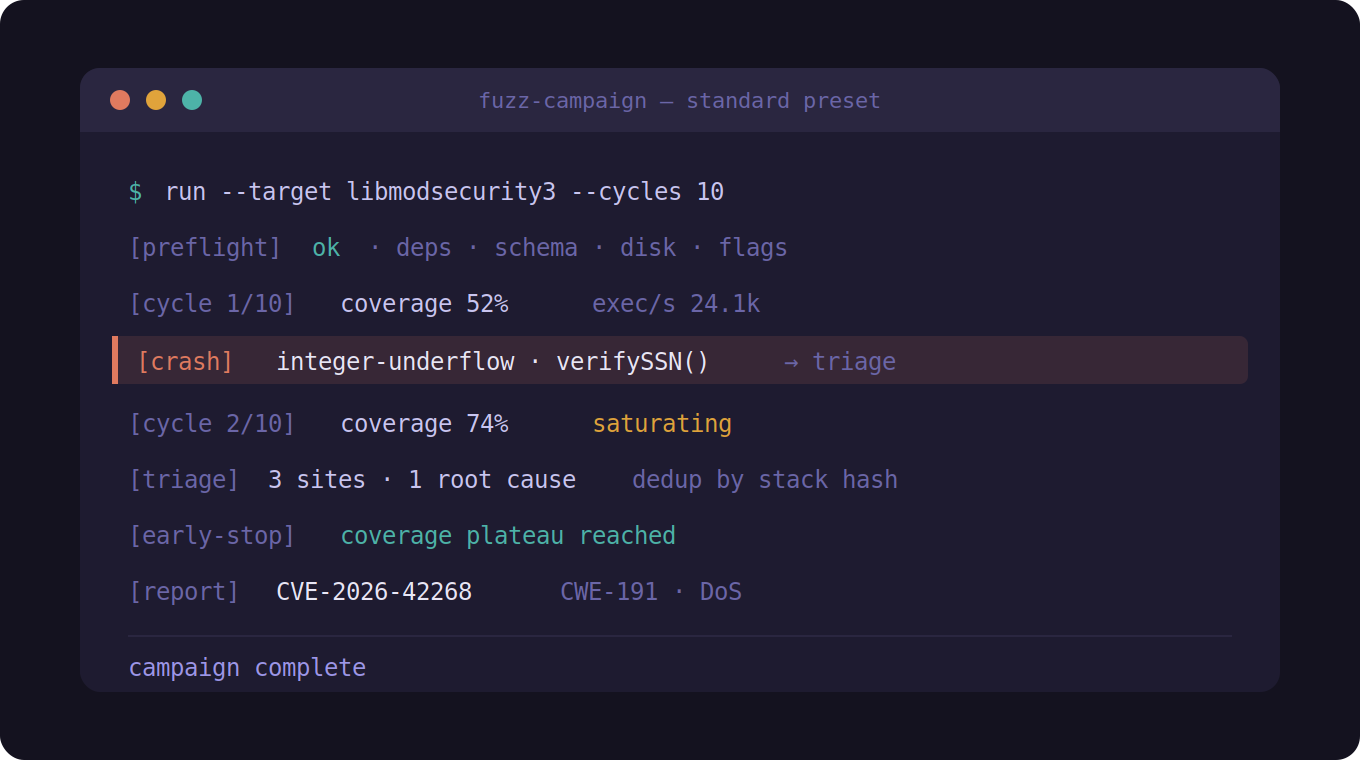
CERT Polska described fuzzlab, a proof-of-concept pipeline that uses machine learning and bounded LLM integrations to automate parts of fuzzing campaign setup, harness generation, crash triage, telemetry, and reporting. The article claims early campaigns found real vulnerabilities in ModSecurity v3 and Oracle VirtualBox, which matters because the useful security lesson is not “agent does security,” but “structured automation can make fuzzing more continuous, observable, and reproducible when operator control is preserved.”
Generated Jaired artifacts are attached below when available.
discussion (0)