1
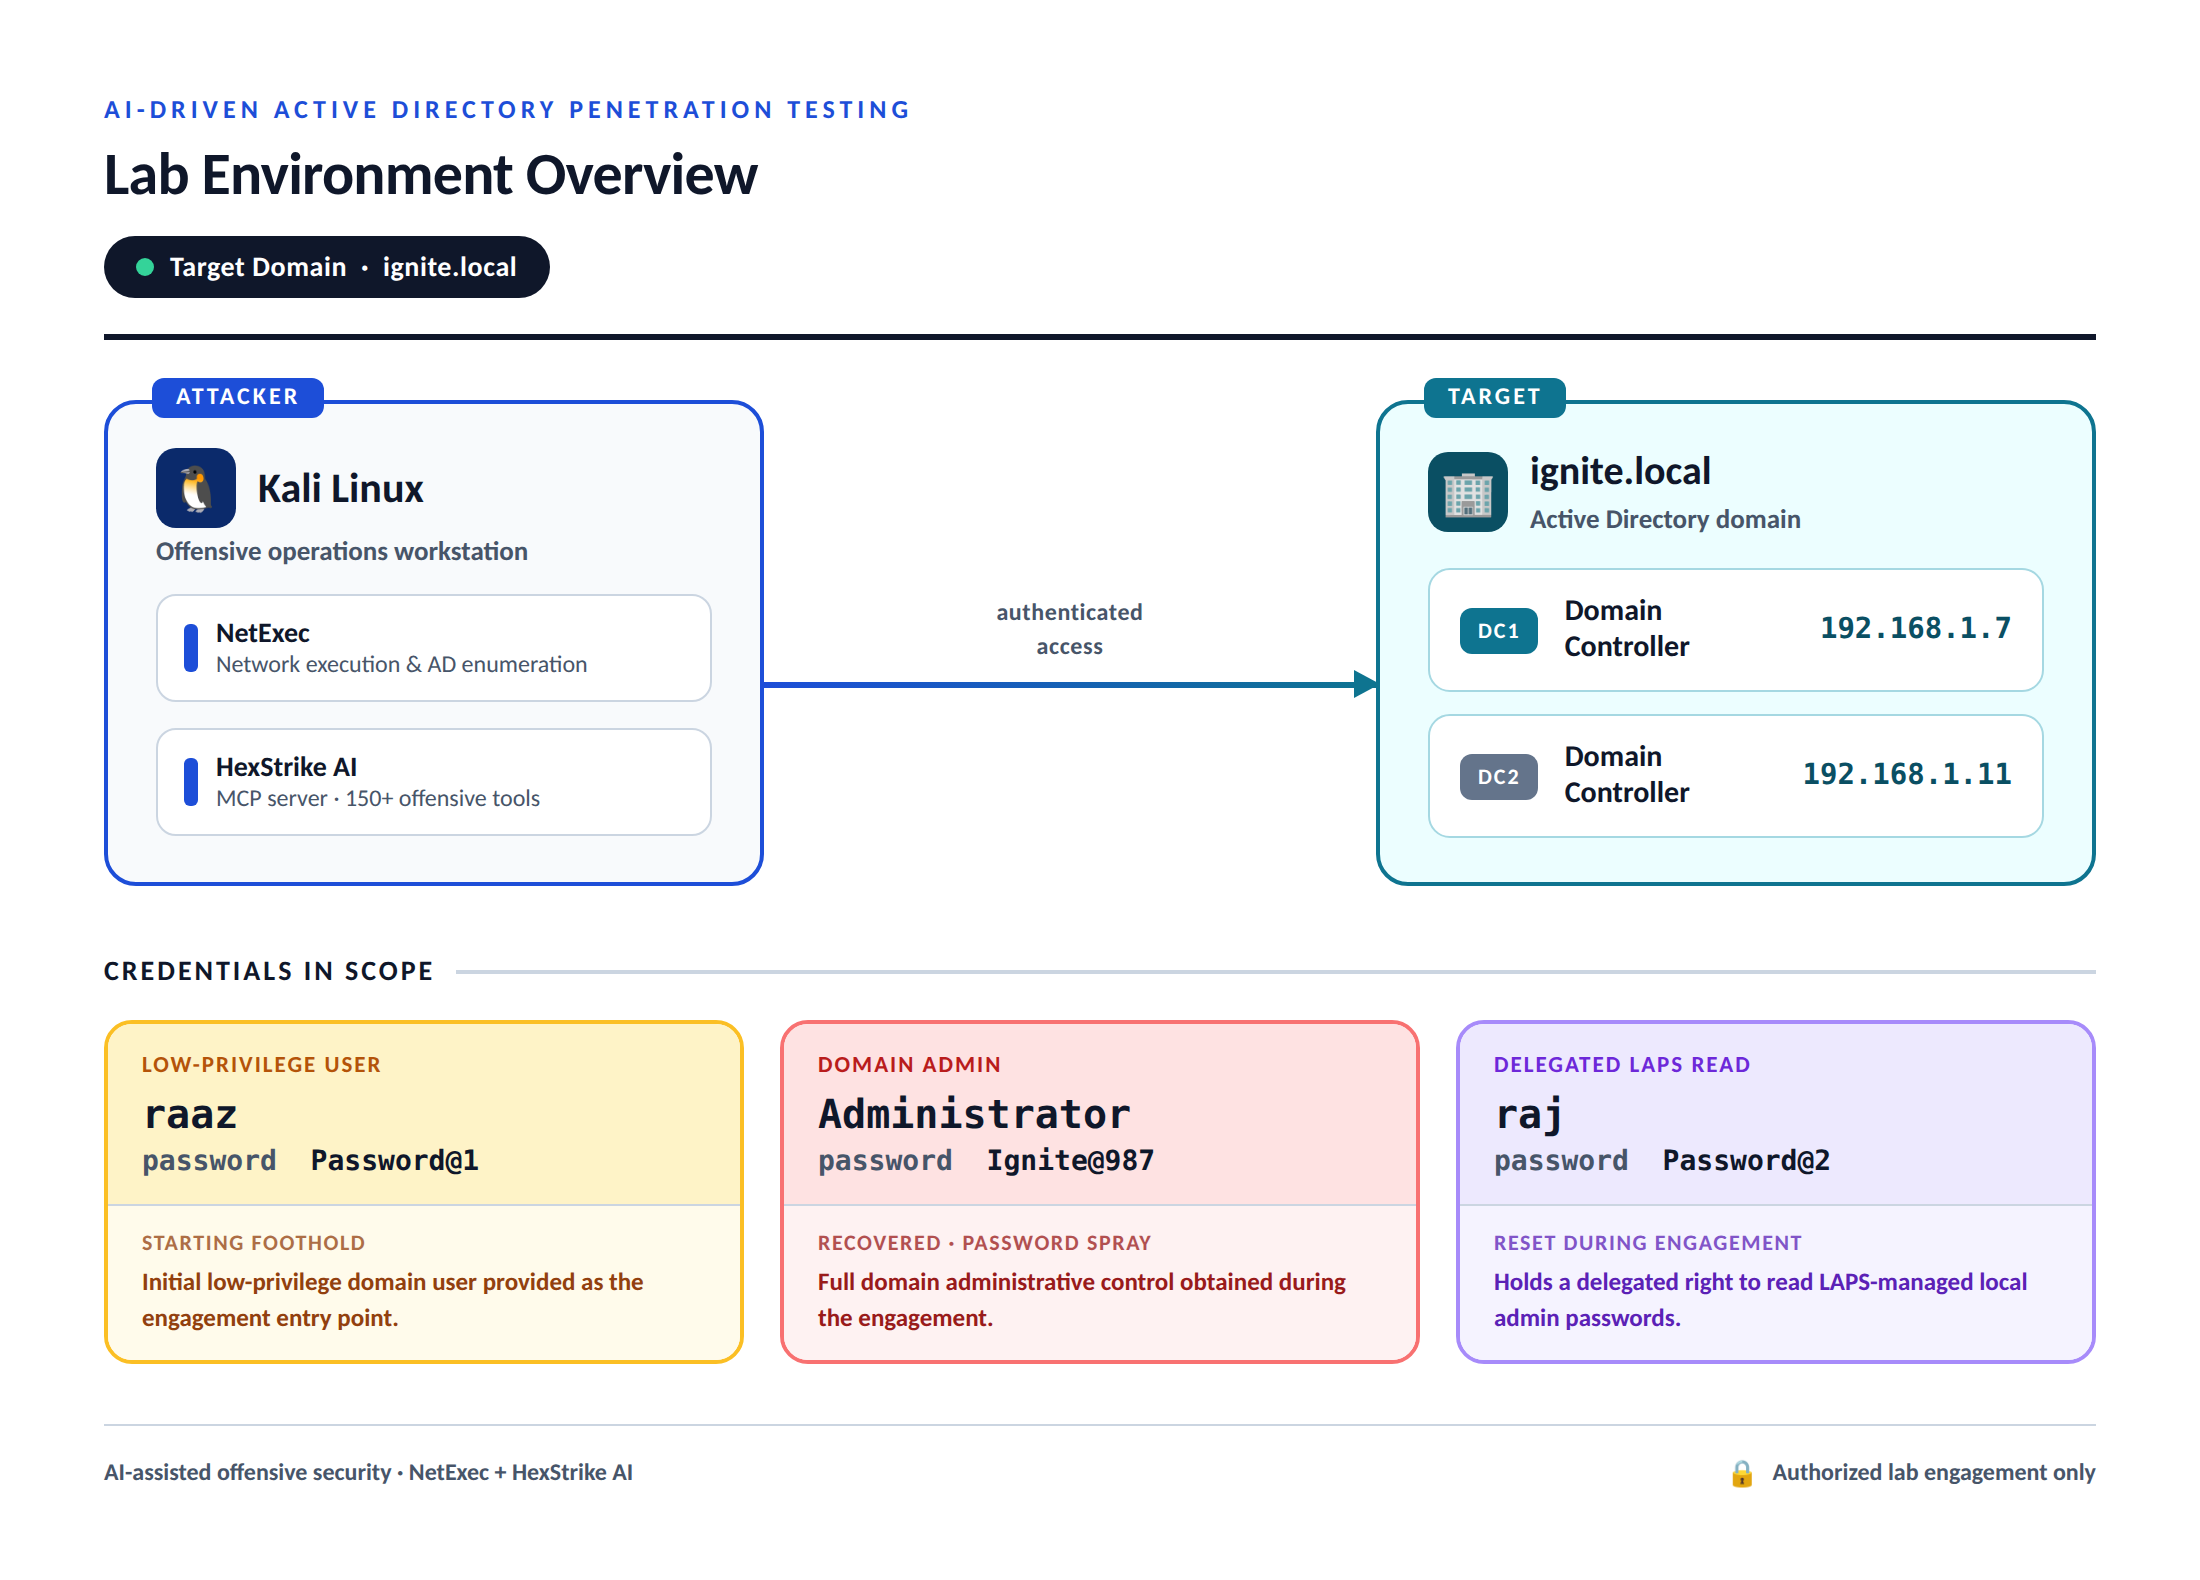
A lab walkthrough chains Claude Desktop, HexStrike AI, and NetExec through AD recon, roasting, password spray, credential dumping, and event-log review. The strong part is the before-and-after discipline around prompts and Windows events, while the caveat is that the evidence is a controlled lab with the model driving real offensive modules underneath.
discussion (0)