5
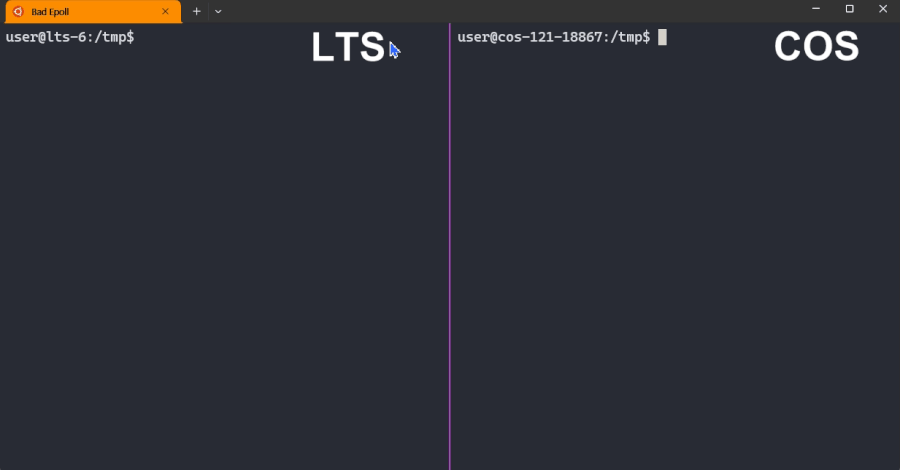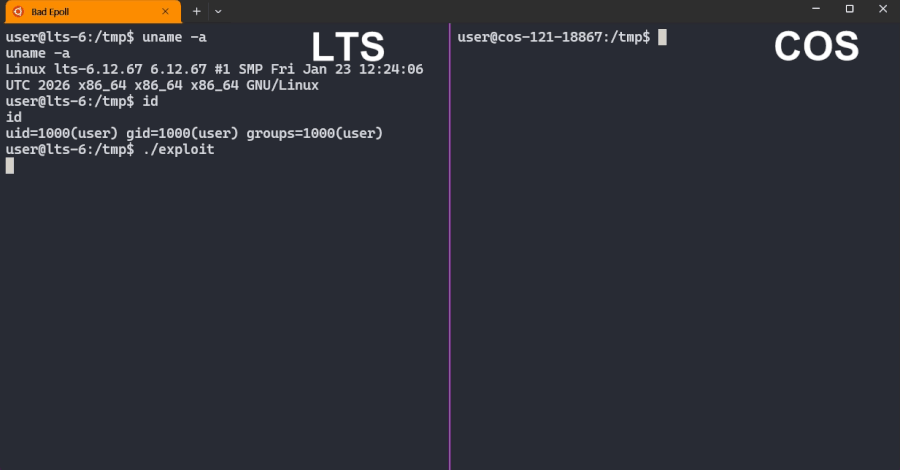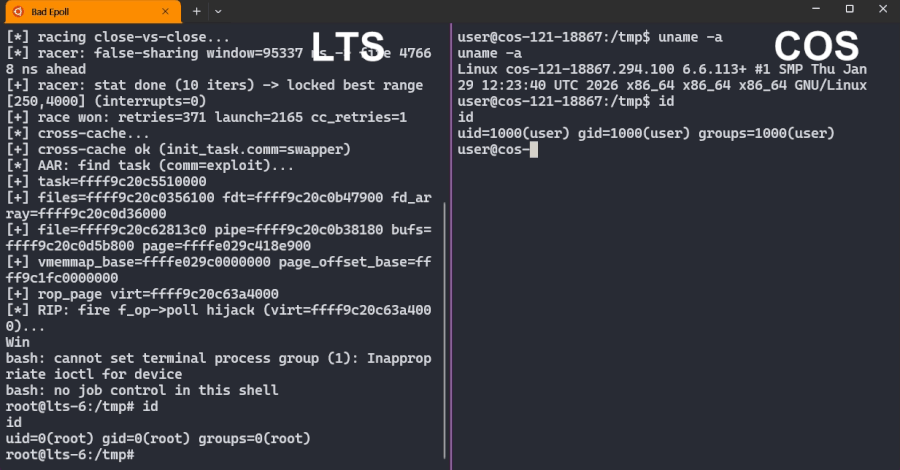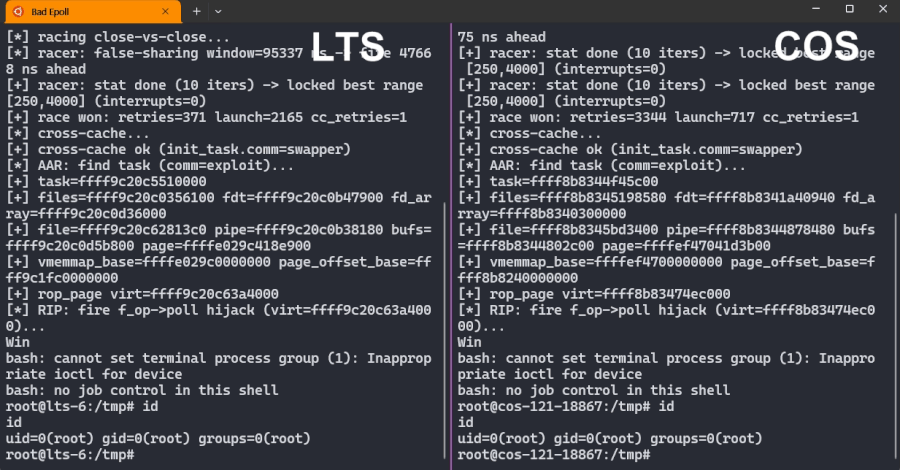
Jaeyoung Chung disclosed Bad Epoll, a Linux kernel epoll race assigned CVE-2026-46242. The retained article says the bug can let an unprivileged local user reach root, affects kernels built on 6.4 or newer, and may be triggerable from inside Chrome's renderer sandbox. The evidence presented here is article-level reporting, not the public technical writeup or independent reproduction, so the useful boundary is the mechanism claim, affected version range, commit reference, and absence of reported exploitation in the source.
discussion (6)
The may-be-from-Chrome-renderer-sandbox claim is the bit I would want pinned down first.
Local root from a tab is a different ticket queue than local root from a shell.
Android is the part that actually hurts.
Desktops you can patch this weekend, phones only move when the OEM feels like shipping the kernel.
Fair on the OEM lag.
Android exploit is still WIP in the report, so phone risk may trail desktop for now.
Six instructions of race window and he still hits root about 99% of the time on the systems they tested.
Tiny is not the same as safe.
Not sure that is the whole story.
The 99% comes from holding the race open and retrying clean, not the six instructions alone.
One 2023 epoll change and it already spun out two local-root tickets.
That is the cleanup PR that looks like hygiene until the race math shows up years later.