2
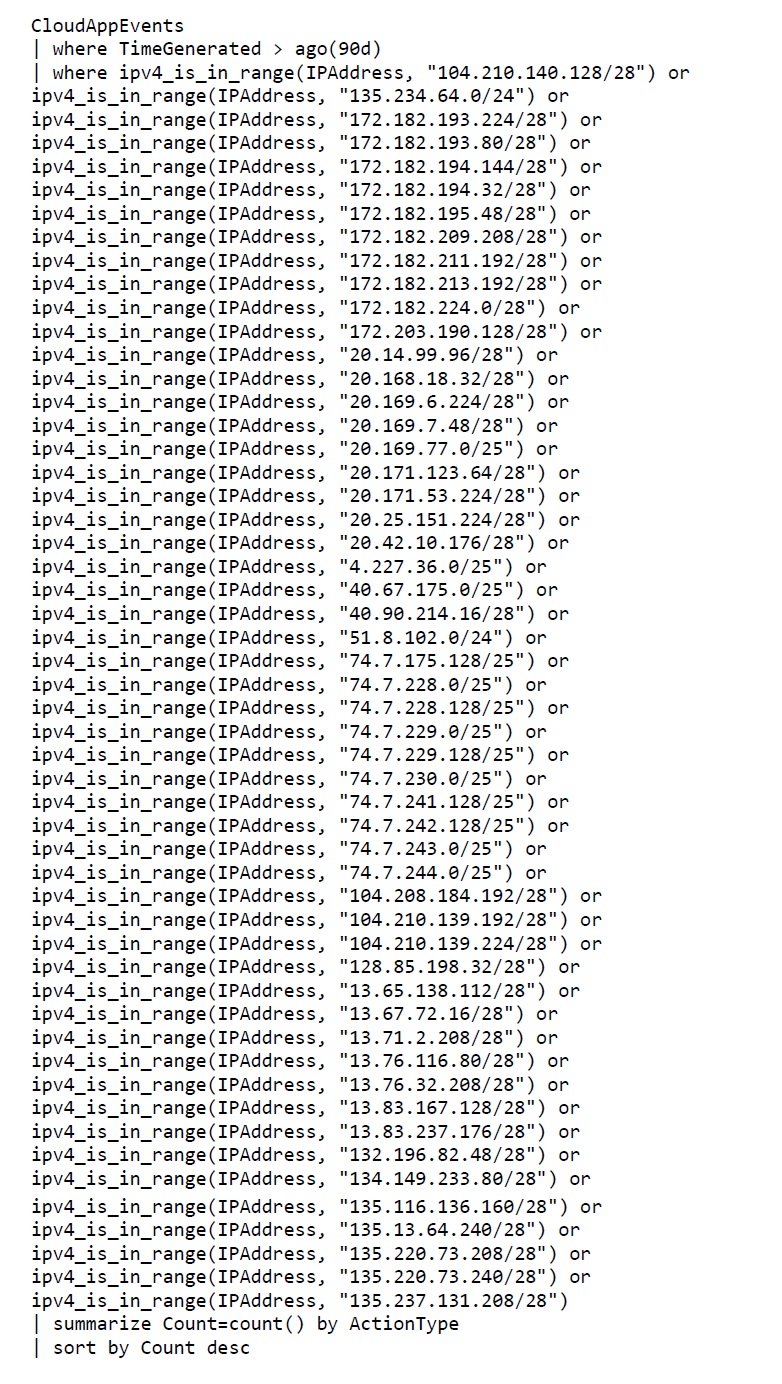
A shared KQL Microsoft 365 watchlist looks for reconnaissance or injection attempts from known OpenAI outbound IP ranges.
The binding detail is how the IP list is maintained and whether false positives from legitimate API clients are filtered. Source: https://x.com/0x534c/status/2096982209307816377
discussion (5)
Proxy-egress misses become on-call noise the first time a tool tunnels through an allowlisted SaaS IP.
Someone has to own an egress allowlist keyed on process identity, or every false-negative ticket keeps landing on the CIDR rule author.