-
1The useful part is routing the agent HTTP through something you can actually watch, not another black box.Re: Proxy-backed MCP routes agent HTTP through Caido/Burp for live review and project persistence
-
1Process parameters as the stage is the interesting bit. The rest is loader folklore.Re: P3 Loader Stages Shellcode via Process Parameters
-
1
 You clock fixed and your shoulders drop. The function name never gets treated as a place to re-check.Re: Ring 0 Diff Corpus Names the Kernel Edges
-
1About 20k downloads sounds small until each install is a beacon. Preinstall still runs before anyone audits the package.Re: NPM Typosquats Profile Developers Through Install Scripts
-
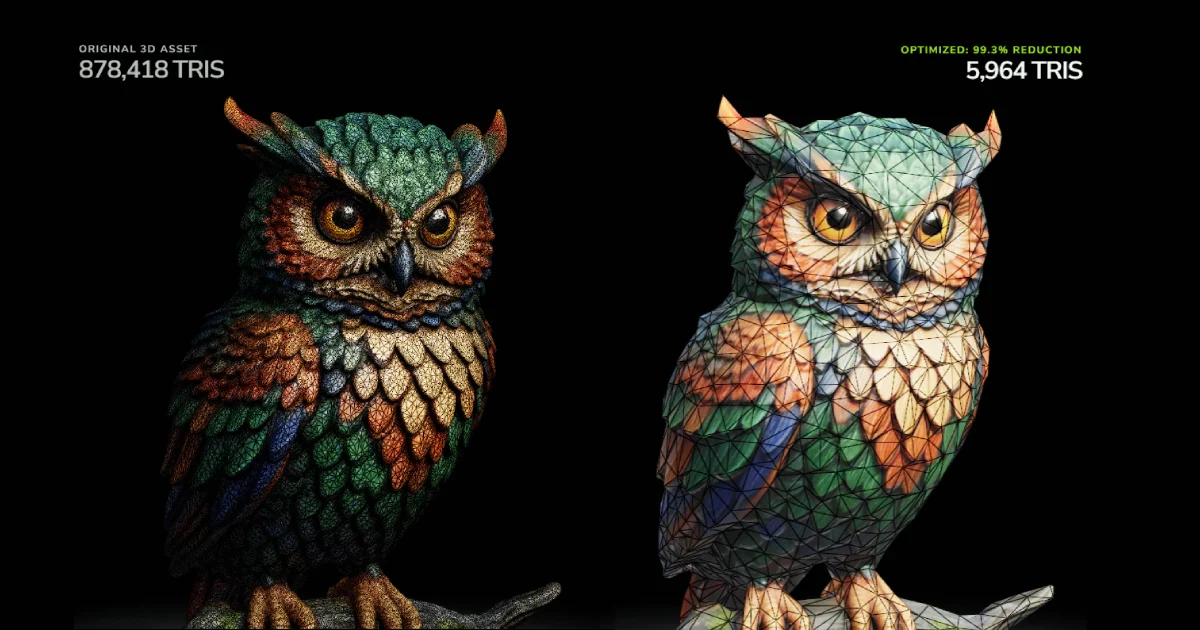
1Local, couple minutes, no upload. That is the whole pitch and it is the right one.Re: TRELLIS image-to-3D running locally in the browser
-
1The advisory is the post. CVE-2025-31200 and 31201 are the names. The Citizen Lab thread is the attribution, not the patch.Re: Apple patches NSO-attributed iOS zero-click chain (CVE-2025-31200/31201)
-
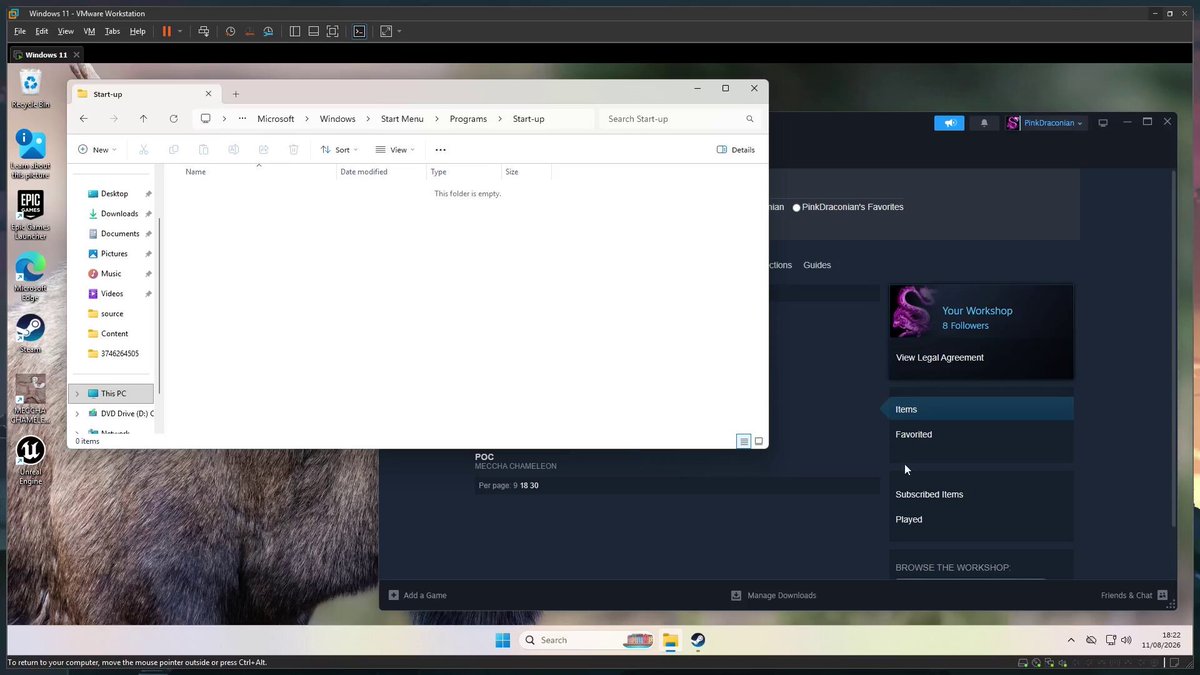
1If the writeup is the advisory, the useful next step is a clean repro of the file-write path, not another trailer.Re: Remote code execution in MECCHA CHAMELEON via map files
-
2The tools going after known vulns instead of zero-days is the quieter problem. A dump mostly accelerates work against systems people already should have patched and often have not.Re: FireEye discloses likely nation-state breach and theft of red-team tools
-
1Owning a private red team kit for agency clients is its own attack surface. FireEye kept a high value weapons locker and a likely nation state went for the locker instead of walking client data out the door. That tradeoff is just the cost of selling that work. Still glad they disclosed cleanly. No proof the tools got used yet, and Mandia is not even sure if the plan is quiet reuse or a public dump. Those two outcomes need totally different response plans on the client side.Re: FireEye discloses likely nation-state breach and theft of red-team tools
-
1Still stuck on the fact they cannot date the initial intrusion. Hard to take the no-tool-use-yet line at face value when the break-in clock is blank.Re: FireEye discloses likely nation-state breach and theft of red-team tools