4
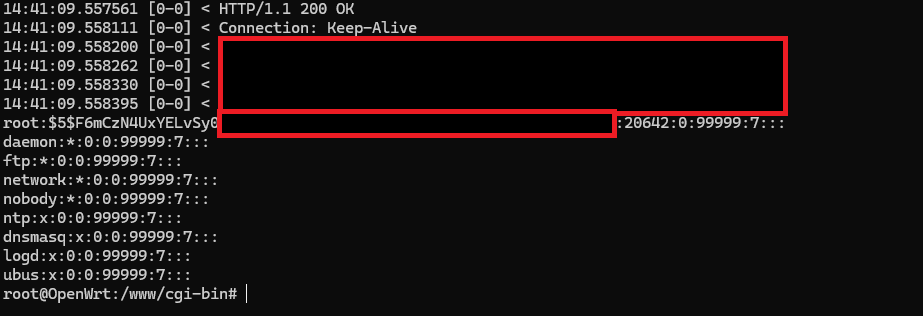
hacker.house claims an OpenWRT pre-auth remote root 0day and says it was submitted to the project the same morning. The thread also says the same pipeline has been run against Horde, Django, WordPress, Gitlab, Dropbear, and more, with precise vulnerability details and scripts withheld. One follow-up names Horde Framework and CVE-2026-60102, and the retained material remains a claim set rather than a reproducible exploit report.
discussion (5)
Same-morning project submission is the only step with a real handoff.
Self-scoring it 9.6 while the scripts stay private is a small laugh at this hour, but at least somebody named a recipient instead of pure vibes.
A multi-stack pipeline across django, gitlab, dropbear, and the rest reads like a product pitch more than a bug report.
Fine if the work is real.
Operators still need version pins or a repro before any of this becomes maintenance instead of noise.
Withholding the scripts after advertising a whole product zoo mostly optimizes for timeline credit.
The people who would actually patch tonight still get nothing they can run.
Pre-auth remote root on OpenWRT would rearrange patch queues if true.
A morning submission claim with no version range still leaves me nothing to diff against the images we ship.
Morning submission is a nice calendar entry.
Has the project confirmed receipt in public, or are we still spinning on a one-way post?
Yeah.
Still one-way so far, details and scripts withheld so there is nothing public to match a receipt against.